
For years, enterprise security teams have invested in technologies designed to identify suspicious activity across increasingly complex environments. Yet one question remains difficult to answer: How do organizations know whether their defenses would actually detect an attack?
The presence of monitoring tools and detection rules does not guarantee that the right information is being collected. Logs can be missing, telemetry pipelines can fail, and detection logic can overlook activity that should trigger an investigation. These problems become even more consequential when organizations begin relying on AI agents to handle security operations.
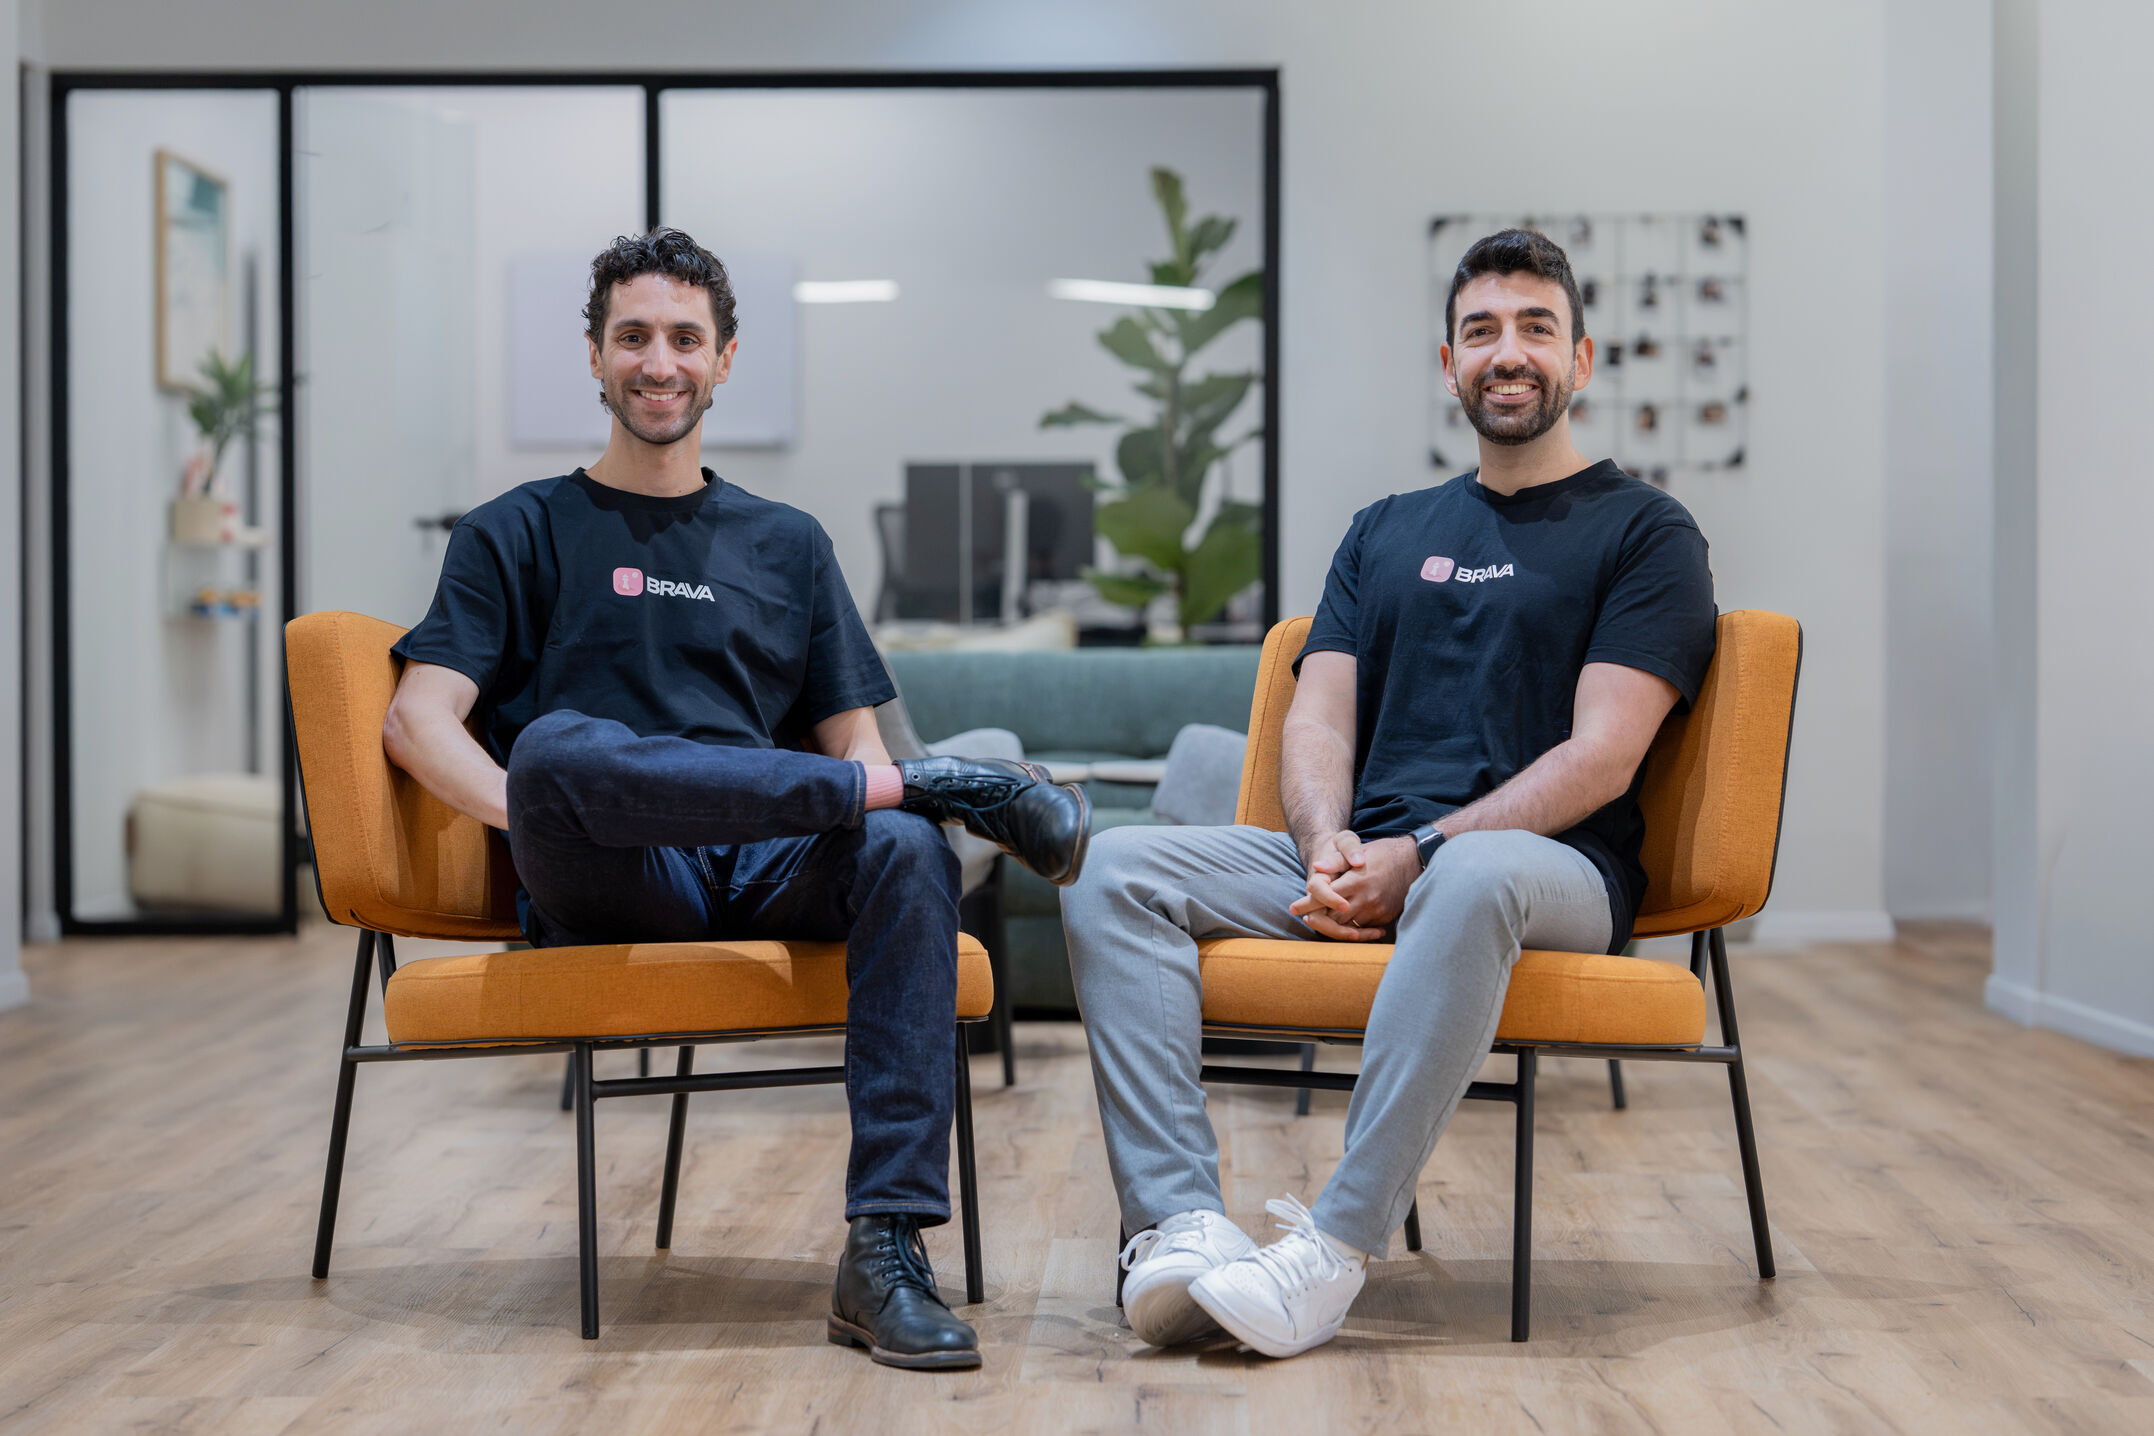
Brava Security is positioning itself around that overlooked part of the cybersecurity equation. The company has emerged from stealth with $15 million in funding led by F2 Venture Capital and Pitango VC, alongside a platform designed to establish the ground truth that security operations centers (SOCs) need. The news of the funding was first reported by Axios.
Its multi-agent AI technology generates the exact telemetry an attack would produce without executing it. By examining that evidence, Brava can show enterprises which attacks their defenses would miss and help correct the underlying detection gaps.
The Limits of Automating an Incomplete Security Environment
The cybersecurity industry’s interest in AI-powered operations is growing, but automation introduces a dependency that organizations cannot afford to overlook: the quality of the data feeding their systems.
As enterprises adopt cloud services, AI applications, and AI-assisted development tools, the number of sources generating security telemetry continues to expand. Security teams must ensure that relevant logs are collected, pipelines remain functional, and detection rules accurately identify suspicious activity.
When those components fail, the consequences can extend beyond an individual missed alert. An organization may have no indication that a particular attack technique occurred, leaving its investigation and response capabilities without the evidence they need.
Brava CEO and co-founder Idan Basre says the industry has focused heavily on automating security decisions without sufficiently proving the quality of the information behind them.
“Everyone is racing to put AI in charge of the SOC. You can’t automate a decision based on evidence no one ever proved,” said Basre, who encountered the problem firsthand while leading product management for Microsoft Defender. “We’re solving the problem that comes before AI can make the right decision: making sure the security infrastructure actually sees the threats it’s supposed to detect.”
A Different Way to Evaluate Detection Coverage
Brava’s platform is built around modeling attacker behavior rather than relying exclusively on alerts generated by existing security products.
Its technology determines how different attack techniques should appear across a customer’s environment and log sources. It then evaluates whether the organization’s defenses would capture that activity and identifies the components that need improvement.
The platform can rewrite SIEM detections and data feeds that are blind to modeled attacks, while also investigating alongside security teams. Its objective is to help organizations understand the actual performance of their detection infrastructure without forcing them to replace the systems they already operate.
Co-founder and CTO Itay Gabbay sees the challenge as one of understanding what an attack looks like in the context of an individual enterprise.
“The hard part of security was never writing detections. It’s knowing exactly what an attack will look like in a specific environment, across all of its log sources, before it ever happens. That’s the problem our models were built to solve,” said Gabbay.
The ability to generate telemetry without executing attacks is central to this approach. Instead of waiting for an incident or relying on assumptions, security teams can evaluate whether their existing defenses would recognize modeled attacker behavior.
From Technology Development to Enterprise Customers
Brava’s initial customer traction includes Fortune 100 companies across retail, energy, and hospitality. Cushman & Wakefield and WELL Health, one of Canada’s largest healthcare companies, are also among its customers.
The company is emphasizing compatibility with existing security environments as part of its enterprise offering. Its platform integrates with Splunk, Google SecOps, CrowdStrike, and more than 70 other sources and destinations.
Deployment speed is another element of its proposition. Brava reports that customers receive their first insights within 10–15 minutes of onboarding, allowing security teams to begin evaluating the platform without a lengthy implementation process.
At Cushman & Wakefield, CISO Erik Hart highlighted the value of bringing AI into the security team’s existing workflows.
“Our SecOps journey is about applying AI where it makes our people more effective, and Brava sits at the center of that. It investigates alongside our team, bringing evidence together so decisions rest on facts rather than on searching” said Hart.
Founders With Experience in Security Research and AI
Brava’s founding team brings experience from military technology development and enterprise cybersecurity.
Basre is a Talpiot alumnus who spent ten years in Unit 8200 as a threat researcher before moving into product management leadership at Microsoft Defender. His experience exposed how limited access to security data could prevent teams from properly investigating incidents.
Gabbay spent seven years in the IDF building core AI systems, including work on a joint DARPA-Israeli research program.
The company has approximately 20 employees, combining AI researchers and security researchers. Its R&D operations are based in Israel, while its commercial team is expanding across the United States.
Expanding Beyond Its Initial Market
Brava’s $15 million seed round was led by Pitango and F2, with participation from angel investors, including executives from Anthropic, Microsoft, and Check Point.
The funding will accelerate technology development and commercial expansion across North America. The company is also preparing to pursue additional opportunities in financial services and government.
With AI agents taking on a growing role in enterprise security, Brava is targeting a foundational requirement for that transition. Its approach centers on establishing whether security systems can produce the evidence needed to make automated investigations meaningful.